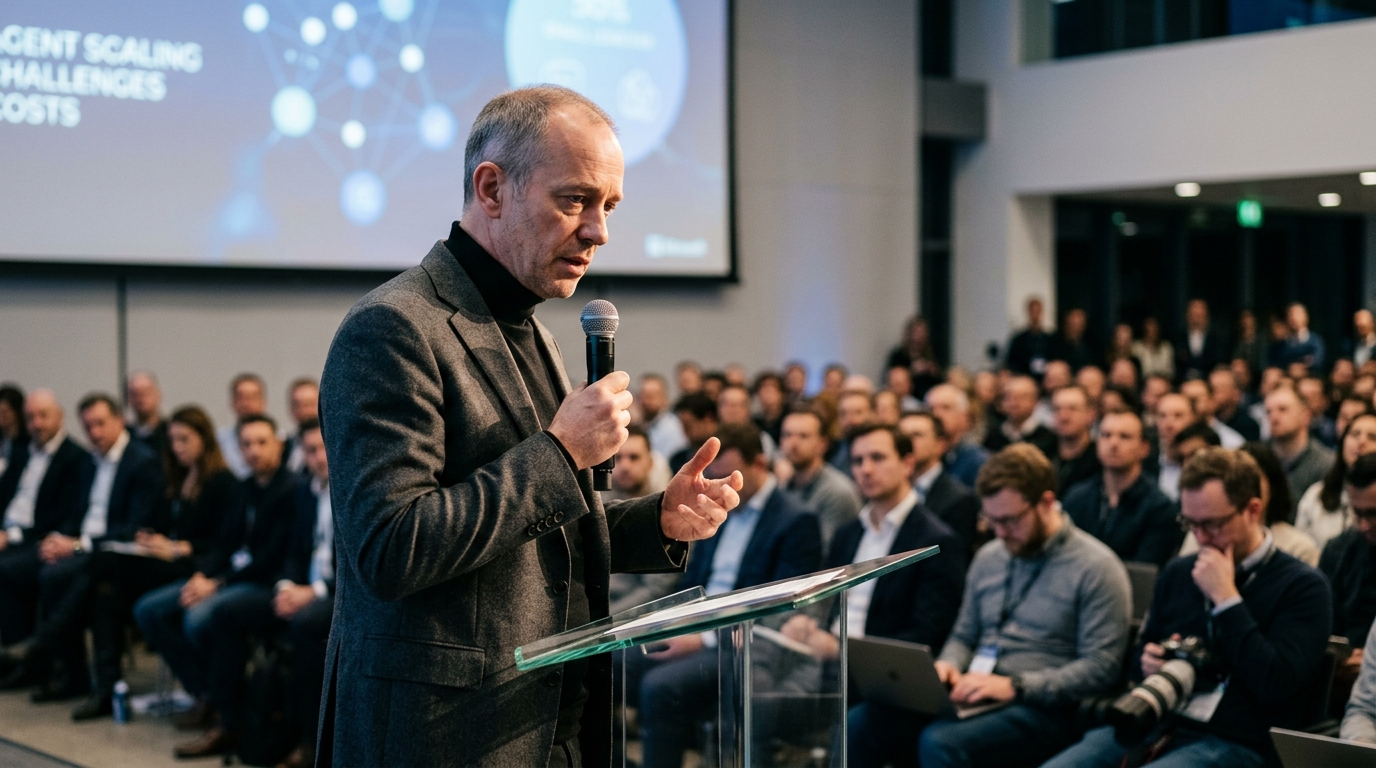
The era of "experimental" Artificial Intelligence is drawing to a close. For nearly two years, global enterprises have been locked in a race to adopt Generative AI, often confined to pilot programs and simple chatbots. However, the next frontier—one that promises true transformation—is AI agents. Unlike simple large language models (LLMs) that merely answer queries, these agents possess the ability to act autonomously, use tools, and complete complex multi-step workflows. Yet, as highlighted at VentureBeat’s recent AI Impact event, the road to scaling these systems is fraught with financial, security, and cultural pitfalls.
The Economic Iceberg: Beyond Token Costs
When an enterprise begins its AI journey, it often focuses on the immediate costs of API calls or model training. This is merely the tip of the iceberg. Brian Gracely, senior director of portfolio strategy at Red Hat, points out that the real cost of AI agents lies in "Day 2 operations." An agent operating autonomously might execute thousands of model calls, retrieve data across multiple databases, and consume compute resources without direct human oversight.
This autonomy leads to an explosion in resource consumption. Companies are suddenly faced with a daunting question: Who controls the budget when an algorithm decides for itself how much compute power to exhaust? Furthermore, there is the issue of technical maintenance. Agents rely on orchestrations that require constant monitoring for errors, model drift, and security patches. The infrastructure cost, particularly in hybrid cloud environments, can quickly eclipse the added value if a centralized management strategy is not in place.
The Security Challenge: Autonomy as a Risk Vector
Security in the age of AI agents is no longer just about protecting data from leaks; it’s about controlling action. When you grant an agent access to your email, CRM, or financial databases, you create new entry points for sophisticated attacks. "Prompt injection" takes on a new, dangerous dimension: a malicious actor could manipulate an agent into performing actions that appear legitimate but undermine the enterprise's integrity.
- Data Exfiltration: Agents often need to move data between disparate applications, increasing the risk of exposing sensitive information.
- Lack of Human-in-the-loop: While full autonomy is the goal, without robust guardrails, a model hallucination could lead to catastrophic business decisions in milliseconds.
- Compliance: Regulators in the EU and US are demanding transparency. How can a company explain an autonomous agent's decision if there is no audit trail of its logic?
"Security cannot be an afterthought. In the world of AI agents, security is the product itself," was a recurring sentiment at the event.
Cultural Resistance and the "Black Box" Problem
Perhaps the most significant hurdle is not technical, but human. Introducing AI agents that take over entire processes triggers fear and uncertainty among employees. A corporate culture may reject the technology if it is perceived as a threat to job security or if the AI’s decision-making process remains opaque. Gracely emphasizes that successful companies are those that invest in "trust education."
Employees must see AI agents as collaborators rather than replacements. This requires a paradigm shift: from performing tasks to supervising systems. However, many traditional enterprises are structured in silos, where data and decisions are isolated. AI agents, to be effective, require horizontal access and collaboration—a requirement that often clashes with existing hierarchies and bureaucratic structures.
The Red Hat Strategy: Open Standards and Hybrid Approaches
To overcome these hurdles, the industry is pivoting toward open standards. Red Hat advocates for an approach where AI is not locked into a single cloud provider (vendor lock-in). The ability to run agents on-premise for security reasons, while leveraging public cloud capabilities for scale, is key to long-term viability. Using open-source models allows enterprises to inspect the code, ensure compliance, and reduce costs by fine-tuning models for specific, narrow tasks rather than relying on expensive, general-purpose LLMs.
In conclusion, the transition to AI agents requires more than just a technical upgrade. It demands a new philosophy of data governance, a re-evaluation of economic models, and, most importantly, an honest conversation about the human role in an automated economy. Those who manage to balance innovation with security and culture will be the leaders of the next decade.